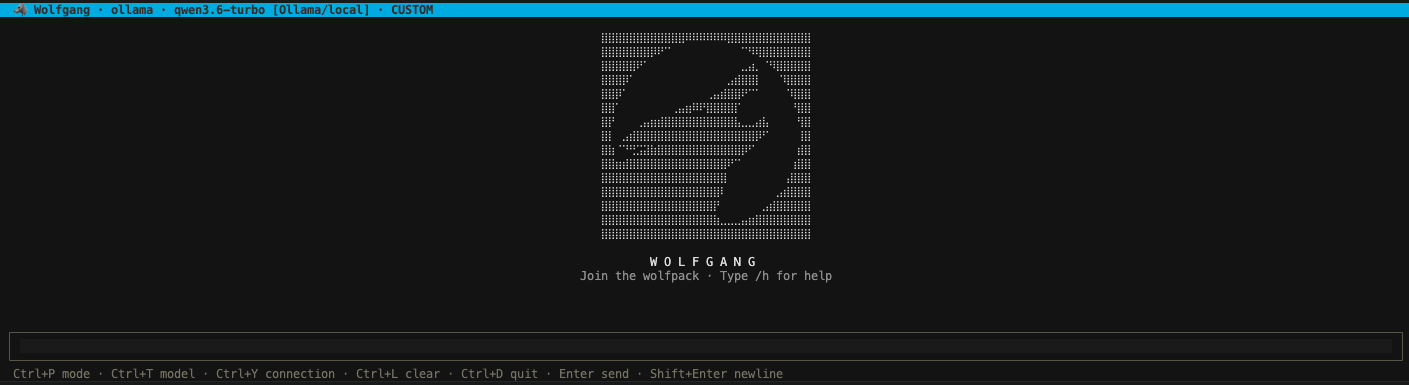
The terminal interface on first start, here running against a local model.
In development · not yet open source
The coding agent that can prove it is locked down — with local models or any hosted API. Not released yet; we intend to publish it as open source.
Runs in a container it cannot edit.
Every request carries signed, single-use proof of that sandbox — malgra can refuse an agent that is not contained.
End to end between wolfgang and malgra, streamed tokens included.
Text from tools and web pages is labelled, so instructions hidden in it are blocked.
malgra's signed receipt shows what it redacted and where the request went.
The terminal interface on first start, here running against a local model.
How it talks to malgra
wolfgang speaks malgra's protocol itself — no plugin, no extra dependency. Any OpenAI-compatible client can use malgra; wolfgang additionally encrypts the payload end to end, signs who is asking, and shows you what the gateway did.
A per-session AES-256-GCM key, wrapped with the gateway's RSA-2048 key, encrypts every request and every streamed token. Pin the gateway's key and the channel holds even through a proxy you do not trust. Tokens still arrive live.
Your API key says who pays. The agent's own signing key says who is asking: each request carries a signed attestation bound to the exact prompt, valid once and for at most two minutes.
malgra reports what it did — personal data it replaced, the route that served the request, the policy profile — and signs a receipt. wolfgang verifies the receipt and shows it in its header, counts only, never the data itself.
wolfgang ── POST /secure/handshake ─────────────▶ malgra
         ◀── { session_id, RSA-2048 public key } ──
         ── RSA-OAEP-wrapped AES-256 key ────────▶  /secure/handshake/finish
         ── nonce ‖ AES-256-GCM(request) ────────▶  /chat/completions
            Authorization: Bearer <api key>
            X-Malgra-Attestation: <signed, single-use>
         ◀── encrypted frames ── decrypted into live tokens
         ◀── X-Malgra-PII · Route · Profile · Tenant · Receipt
[[custom_models]]
name         = "eu-coder"
endpoint     = "https://api.eutonomous.eu/v1"
backend      = "malgra"
model_id     = "scaleway/qwen3-coder-30b-a3b-instruct"

# who pays: your eutonomous key, from the encrypted secret store
api_key      = "${secret:EUTONOMOUS_API_KEY}"
# who is asking: this agent's own key signs every request
jwt_alg      = "RS256"
jwt_key_file = "~/.wolfgang/agent.key"
jwt_sub      = "wolfgang-laptop"
The example uses the eutonomous API, which is not open for inference yet. The same configuration works against a malgra gateway you run yourself.
wolfgang and malgra
Any client gets malgra's server-side protection. A client that can also vouch for itself lets the gateway go further: it no longer has to guess what kind of environment the agent runs in — it can check.
wolfgang starts the agent in a container you define: no network or only the hosts you allow, project files read-only unless you say otherwise, individual tools switched off.
The launcher, outside the container, signs a description of that sandbox with a key that is never mounted inside it. A compromised agent cannot write itself a better one.
Each request carries a short-lived, single-use signed attestation that malgra checks before serving it. A key can require one, so an agent that is not sandboxed is refused.
wolfgang marks which parts of the conversation came from tools and web pages. malgra treats those strictly as data: an instruction inside them is blocked, while the same words typed by you are allowed.
None of this is reserved for wolfgang. The attestation and labelling formats are documented, and any client can implement them — wolfgang will simply be the first. Until then, every client gets malgra's server-side features in full.
The agent
Ollama, LM Studio, llama.cpp or vLLM with no account and no network, or any OpenAI- or Anthropic-compatible API. Switching is one command; the tools and workflow stay the same.
Plan mode, bounded step limits, parallel tool calls, sub-agents, and self-checking that runs your tests after it edits.
Tiered approvals with diff previews before changes land, your own pre- and post-tool hooks, and one-key undo when you change your mind.
MCP and SMCP tool servers, composable skills with allow-listed tools, and a graph memory that carries across sessions.
Provider keys live in an encrypted store and are referenced from the config by name, so a config file can be shared without them.
A rich terminal interface, a classic command-line REPL, or a non-interactive mode for scripts and CI.
wolfgang is in private development. If you would like to test it against your own codebase or your own malgra gateway, write to hello@eutonomous.eu.